
This article deals with the Filters and GeoIP features of WEDOS Protection. For Web Application Firewall settings see WAF and Combo Rules.
In this article, you will learn:
WEDOS Protection Features
To protect your web, WEDOS Protection proxy servers use the following features:
- Filters: Using filters, the system blocks a wide range of threat types. You can also filter traffic directed to specific URLs on your domain. To learn more, check out Filters.
- GeoIP: This feature expands filters, enabling you to allow or block incoming requests from IP addresses by country. To learn more, check out GeoIP.
These features are in Режим AI by default. This means that any event recognized as a threat automatically informs the entire system’s decisions on how to handle it. Users with the Expert subscription plan and above can enable Custom settings in addition to AI Mode.
Security feature Режим AI cannot be disabled.
Protection Feature Setup
To access the feature settings, follow these steps:
- Log into the WEDOS Global Admin panel ⧉.
- Select a domain or template to set up.
- In the left menu, select the feature to set up.
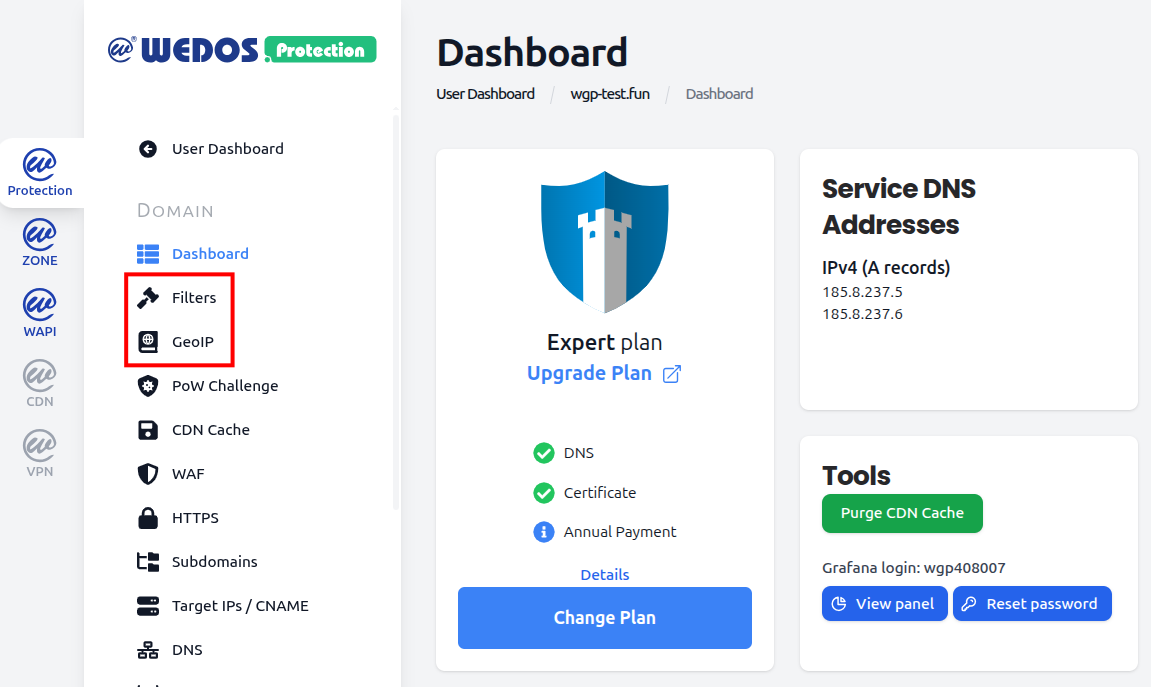
Filters
WEDOS Protection currently uses the following filters:
- IP Filter: Traffic coming from IP addresses or ranges listed here are blocked by the proxy and do not reach your web server. This filter is especially helpful if an attack is coming from a single IP address or small subnet.
- Фільтр ASN: In addition to IP addresses, you can also block traffic from selected Autonomous System Numbers. An Autonomous System (AS) is a group of one or more IP prefixes run by one or more network operators that maintains a single, clearly defined routing policy. The network operators must have an ASN to control routing within their networks and to exchange routing information with other ISPs.
- User Agent Filter: User agent визначає тип застосунку, операційну систему або іншу сутність, що запитує доступ до Вашого вебсервера. Зазвичай вони ідентифікують себе за допомогою
User-Agentheader. Attackers may fake this header to announce themselves as a different client (agent spoofing). - URL Filter: This filter sets up protected URLs on your domain, blocking any incoming traffic to the filtered addresses. In this regard, it works differently from the filters above.
- JA4 TLS Fingerprint Filter: Відбиток JA4 створюється на рівні TLS-термінації та дає змогу класифікувати стек клієнта, а не лише заголовок. Послідовно фіксуючи та хешуючи ці характеристики, Ви отримуєте стабільний відбиток, прив’язаний до клієнта technology stack (бібліотека TLS, ОС, середовище виконання), а не на заявлену ним ідентичність. Цей фільтр особливо корисний для уникнення хибних спрацювань.
- JA4H HTTP Fingerprint Filter: This is the same as JA4 but based on a client’s HTTP request. This filter is especially helpful for catching bots that match a browser at the TLS level but expose themselves at the HTTP layer.
- Referer Filter: The Referer HTTP header indicates the page or domain that linked to the current request. Useful for blocking referral spam, content scrapers, or traffic originating from known malicious or unwanted domains. Commonly used to prevent hotlinking (інші сайти, що вбудовують Ваші зображення, відео чи ресурси напряму), а також для припинення фальшивого реферального трафіку, який спотворює аналітику.
- Content-Type Filter: The Content-Type HTTP header declares the format of the request body (e.g.
application/json,multipart/form-data,application/x-www-form-urlencoded,text/xml). Useful for restricting your application or API to only the payload types it expects — for example, blocking file uploads on endpoints that should only receive JSON, rejecting XML/SOAP on JSON-only APIs, or stopping malformed and unusual content types commonly produced by automated tools and exploit scanners. - IP Category Filter: Filters traffic based on the type of network the source IP belongs to, rather than the IP address itself. WGP classifies each client IP into categories such as datacenter / hosting provider, residential ISP, mobile carrier, TOR / VPN / anonymising proxy, search engine crawler, та подібних групах. Це дає змогу застосовувати широкі правила на основі наміру без необхідності підтримувати окремі списки IP-адрес, наприклад дозволити трафік від домашніх користувачів і перевірених пошукових систем, перевіряти трафік із дата-центрів і повністю відкидати трафік TOR/VPN.
- GeoIP filter: Since most IP addresses also carry the information on which country they are allocated to, you can quickly filter for an entire country. Because of its extensive setup, the GeoIP filter has its own section.
When accessed from a browser, blocked devices display an Доступ заборонено error page. Otherwise, the blocked content returns a 456 помилка.
For the Start and Advanced subsription plans, all filters are Режим AI only. To add your own IPs, ASN, User Agents and protected URLs, upgrade to the Expert plan. This will allow you to allow, block, or require proof of work for the filter items you set.
GeoIP
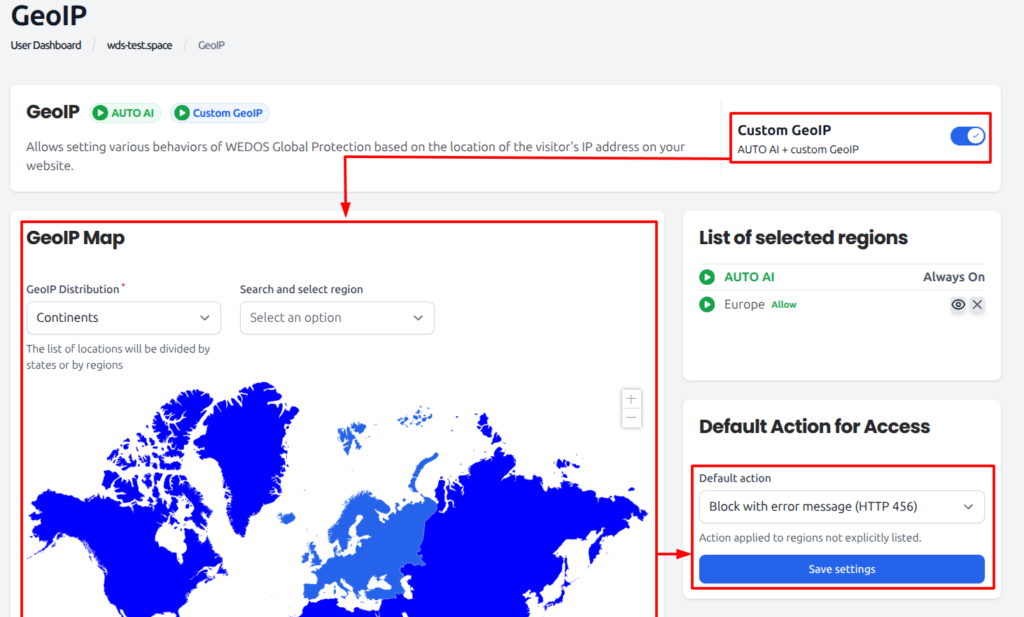
GeoIP is a type of filter which allows you to set up specific rules for specific countries, as chosen on a map. In addition to access (allow or block traffic), the GeoIP filter can also manage where to deploy Proof of Work as a protective measure.
For the Start and Advanced subsription plans, GeoIP is Режим AI only. To unlock the management interface (map), upgrade to the Expert plan.
To set up custom GeoIP rules, navigate to a Domain’s GeoIP interface and follow these steps:
- Enable Custom GeoIP.
- Select a region (continent or country) using the dropdown or map.
- Select one of the following actions for that region and click Submit:
- Allow access / Whitelist: No GeoIP-based block.
- CAPTCHA-перевірка (Proof of Work): Require visitors to complete a challenge (Proof of Work, such as CAPTCHA).
- Блокування з повідомленням про помилку (HTTP 456): Always block traffic, but display customizable error message.
- Блокувати мовчки: Блокувати трафік, повертати лише код помилки.
- Select default action for all other regions.
- Click the Save settings button and Confirm.
FAQ
How do I turn off AUTO AI on Protection features?
AUTO AI завжди ввімкнено. У користувацькому режимі можна додавати власні правила, але AI вимкнути не можна.